Use case · Financial services
Tenant-to-tenant & SharePoint cloud migration
Consolidate Microsoft 365 estates after a merger with identity-first cutover and preserved collaboration.
Key metrics
Results at a glance
Data security
DLP & MIP enforced
Deployment
Zero downtime
Identity
SSO + MFA
Cutover model
Phased waves
Problem statement
The challenge
Two financial brands sat on separate Microsoft 365 tenants after a merger. Mail, Teams and SharePoint were fragmented, SharePoint on-premise blocked remote work, and DLP/MFA policies were inconsistent — putting regulated client data at risk during any rushed cutover.
Architecture solution
How we solved it
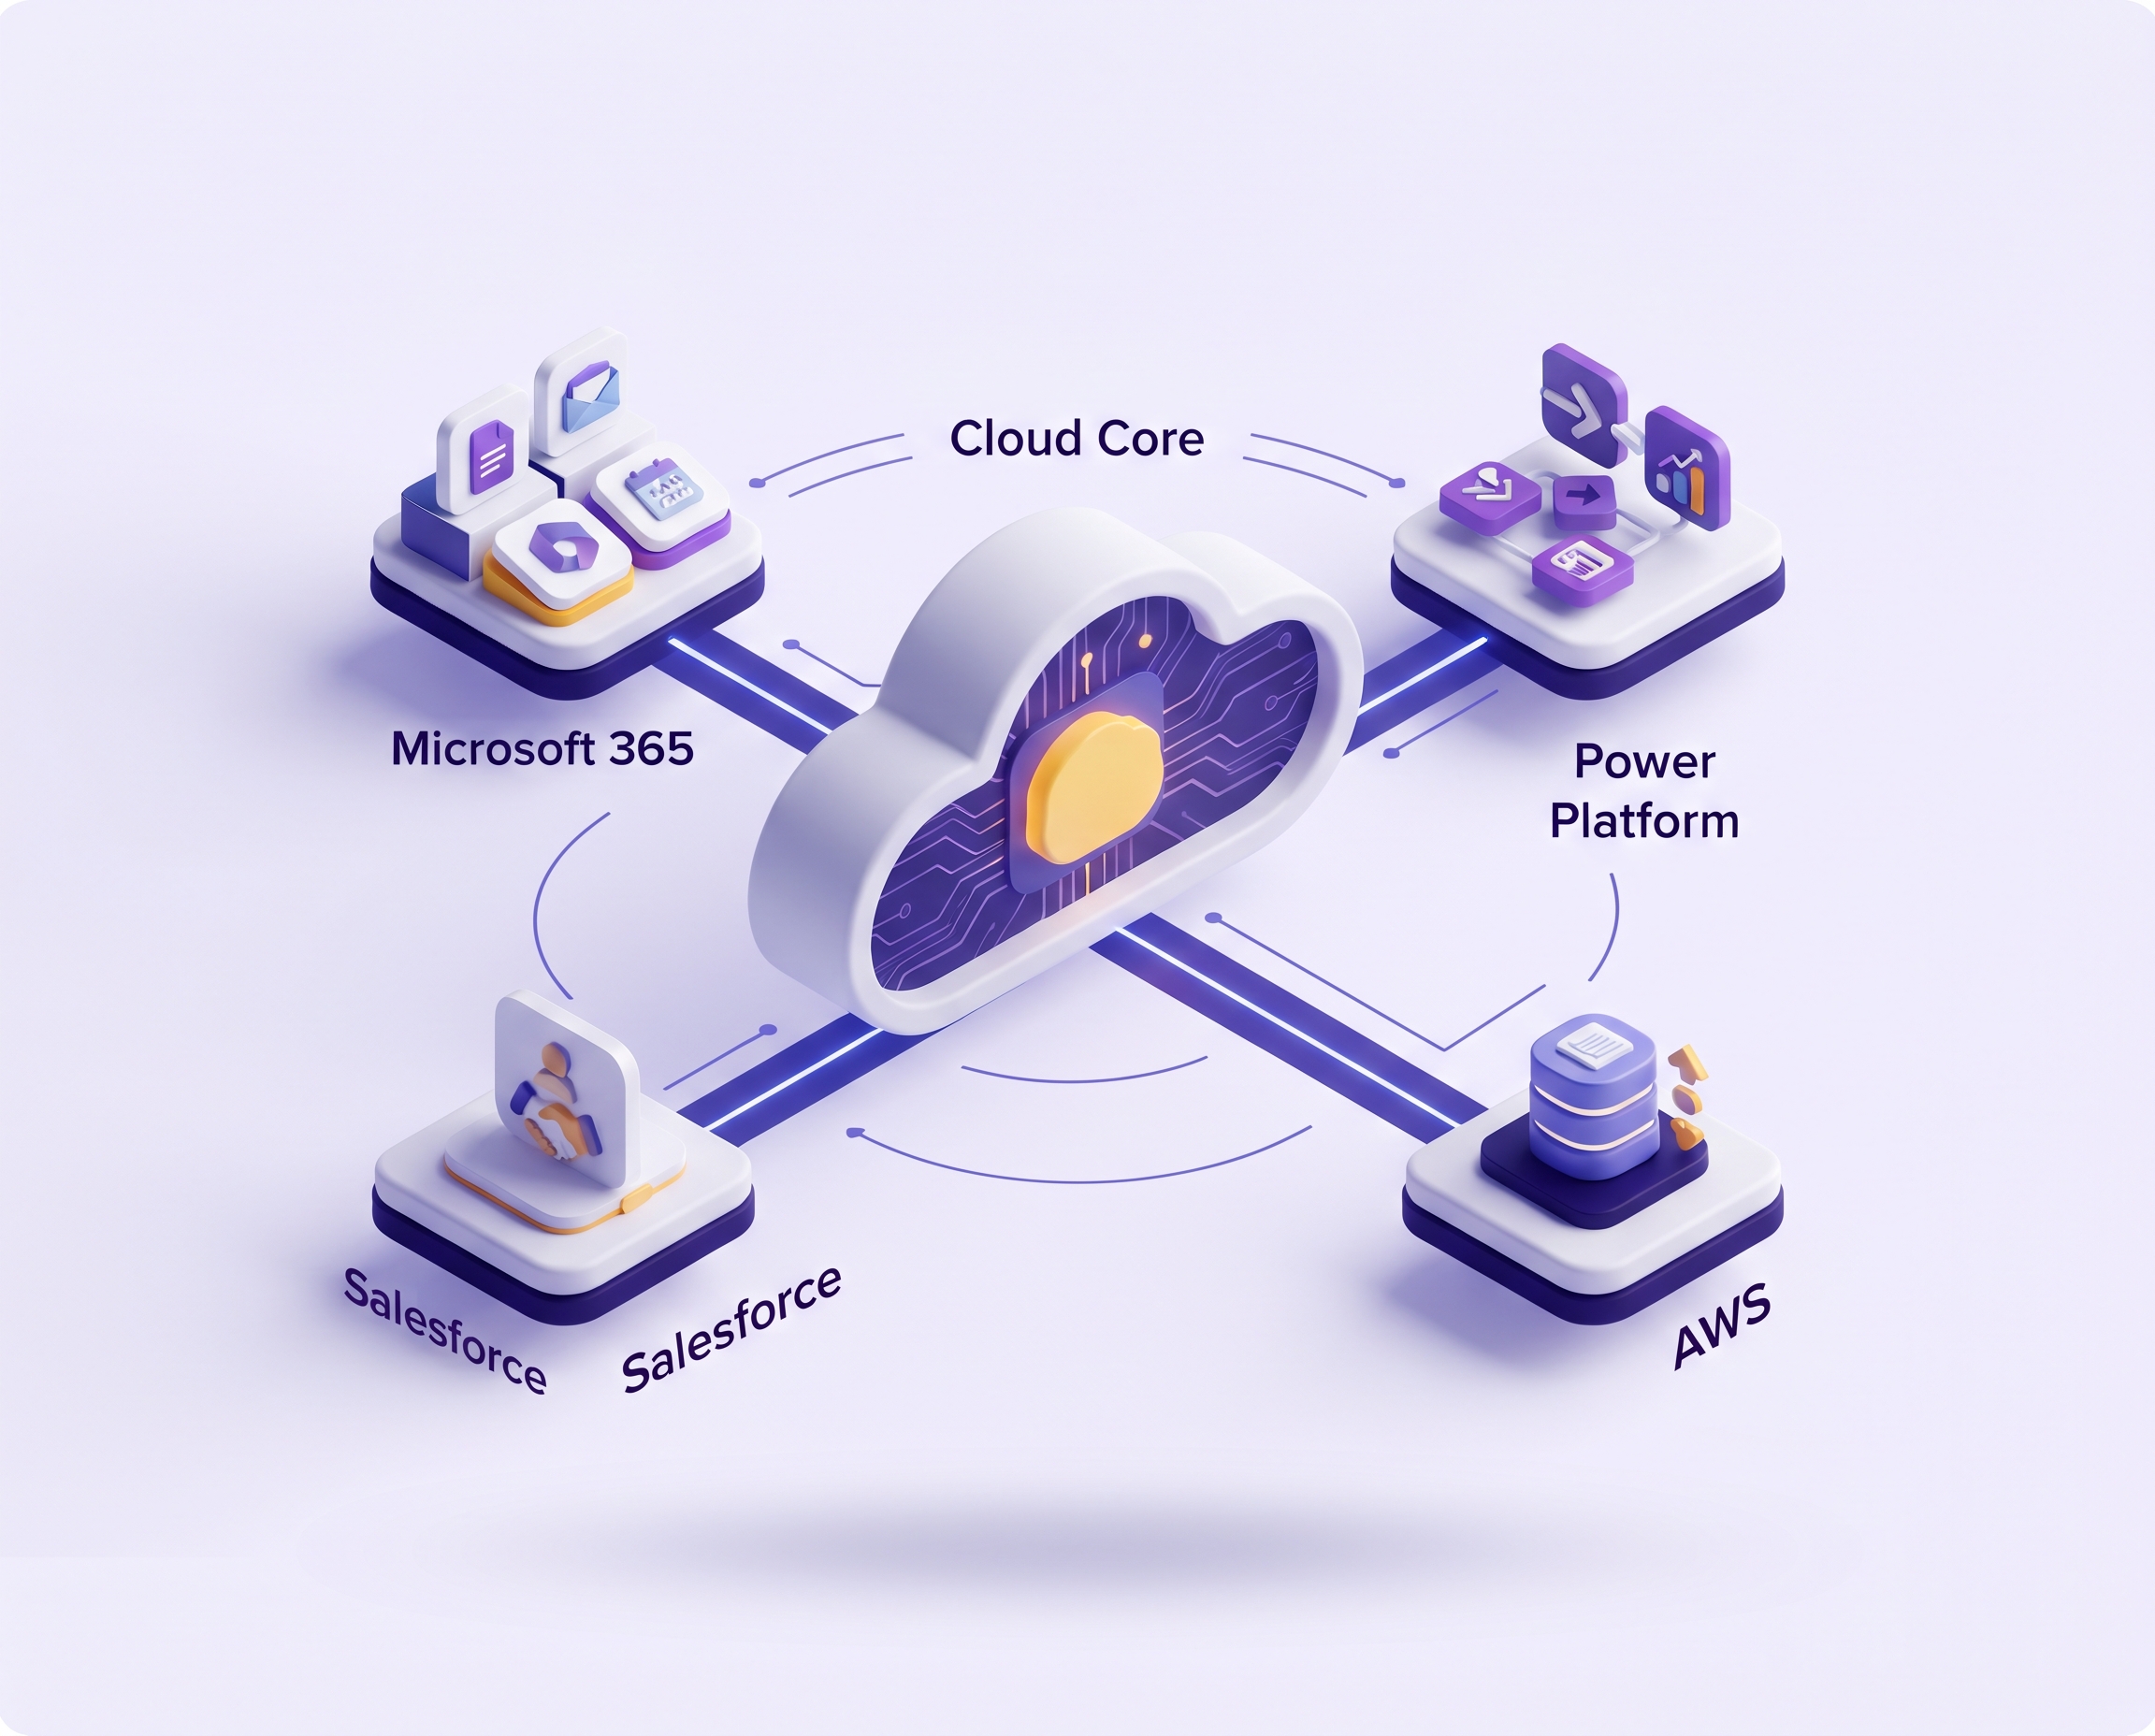
We sequenced identity first (Azure AD Connect, SSO, MFA), then migrated mail and collaboration in controlled waves with rollback paths. SharePoint on-premise moved to Online with permissions and retention labels preserved. Microsoft Purview DLP and MIP labels were applied so policy followed documents across Outlook, Teams and OneDrive.
Business impact
What changed
Staff kept working through the merger instead of waiting on a weekend big-bang. One governed collaboration estate replaced twin tenants, and audit evidence for DLP, MFA and retention was ready for internal risk and external reviewers.
Deliverables
What we put in place
- SharePoint on-premise to Online cloud migration
- Teams, SharePoint & OneDrive enterprise rollout
- Identity setup, Azure AD Connect SSO & MFA
Next step
Want a similar outcome in your organisation?
Share your constraints and we will outline where to start — with scope, timeline and the controls your sector needs.